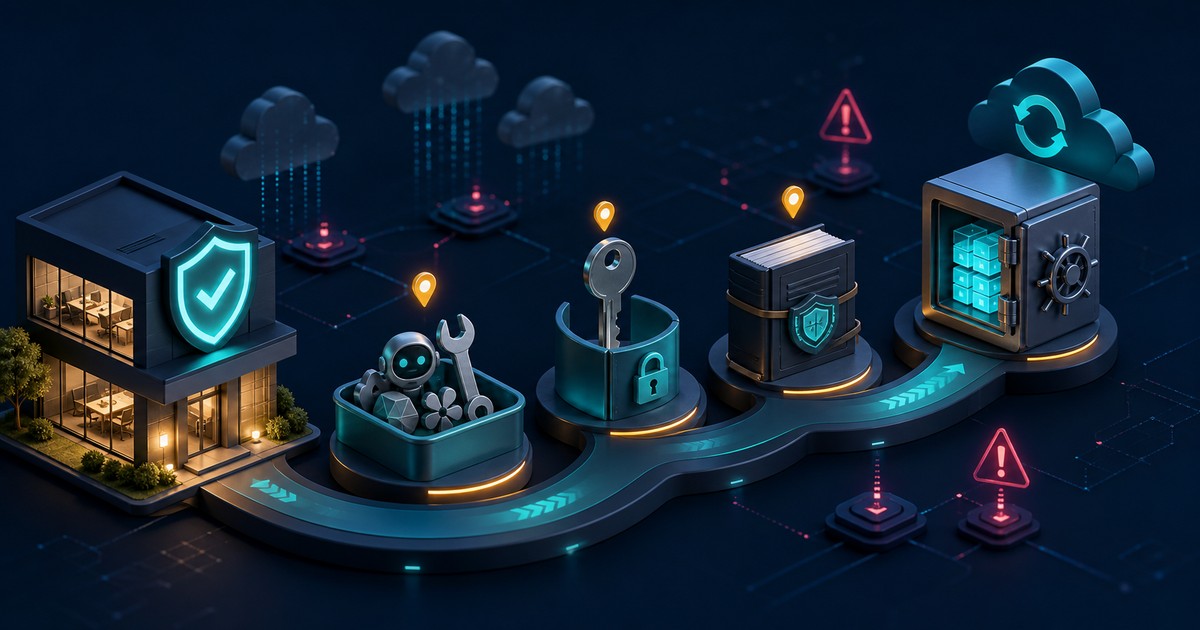
A thirty-day security plan for an AI-enabled SMB should reduce the largest practical risks before adding complex governance. The sequence is inventory, containment, evidence, and recovery. It gives each AI workflow an owner, limits access to what is necessary, records consequential actions, and proves that the business can stop or recover. The plan does not certify the company or guarantee that incidents will not occur.
First week: inventory and contain
List every approved and unofficial use of AI across the business. Include browser assistants, meeting tools, content systems, customer support, code tools, document analysis, and agents connected to business applications. For each entry, capture the owner, users, data categories, vendor, credentials, integrations, action rights, business purpose, and a decision to keep, restrict, or stop.
Prioritize by consequence rather than popularity. A writing assistant that sees public material is different from an agent that reads customer records or sends messages. The medical data security case helps show how access and handling controls can shape a delivery design. It is not evidence that another environment has equivalent protection.
Remove shared accounts, unused tokens, broad administrator rights, and secrets stored in prompts or documents. Give each integration a named owner and the smallest workable permission. Require human approval for payments, access changes, external commitments, deletion, and other difficult-to-reverse actions. Pause any workflow whose data source or authority cannot be explained.
Middle weeks: protect data and create evidence
Classify the information entering each workflow and decide what may reach the model. Prefer references, redaction, or local preprocessing when full values are unnecessary. Record the vendor’s retention and training settings, subprocessor path, deletion route, and support access. Sensitive information should not flow into a free consumer account merely because the interface is convenient.
Add an audit trail for consequential operations. Connect the requesting identity, policy decision, model run, tool call, approval, affected object, and result with a stable identifier. Do not copy every prompt into the log by default. A concise receipt is more useful than an unprotected archive of business content. The precision release shows explicit routing and completion checks. A separate deployment still needs its own security review.
Review third-party rights and obligations alongside technical controls. The font license risk audit shows how a small dependency can create an overlooked contractual issue. Apply the same attention to model terms, uploaded content, generated output, open-source components, and data-processing agreements. Seek qualified advice for legal conclusions.
Final week: test recovery and assign the routine
Choose the most consequential workflow and run a controlled failure exercise. Make the provider unavailable, revoke its credential, return an incorrect result, reject an approval, and stop an integration before it acts. Confirm that people can detect the issue, preserve evidence, switch to a documented manual process, reconcile unfinished work, and return safely.
Turn findings into a small operating routine. Name the person who reviews new AI tools, access changes, log coverage, vendor updates, and recovery evidence. Keep a register of accepted risks and corrective work. Measure completion of controls and tests, not imagined revenue gains or broad transformation. A disciplined plan favors one inspectable workflow with measurable proof over unsupported promises.
At the end of the month, management should have a current inventory, narrower permissions, known data paths, useful action receipts, a tested fallback for the priority workflow, and a short list of unresolved risks. That is a decision base, not a security certification. Repeat the review whenever a new tool, data class, vendor, or action right is introduced.
Frequently Asked Questions
Start with workflows that handle sensitive data, use broad credentials, trigger external actions, affect money or access, or lack a clear business owner.
No. It organizes practical controls and evidence, but applicable legal duties and formal assurance require review against the specific business and jurisdiction.
Prioritize payments, access changes, deletion, external commitments, customer communications, production changes, and other actions that are costly or difficult to reverse.
Keep an inventory, owner decisions, permission changes, data-flow notes, vendor settings, action receipts, exercise results, residual risks, and assigned corrective work.
If you want an independent view of the highest-consequence gaps, book an AI governance and agent audit to turn the month of work into a prioritized control backlog.