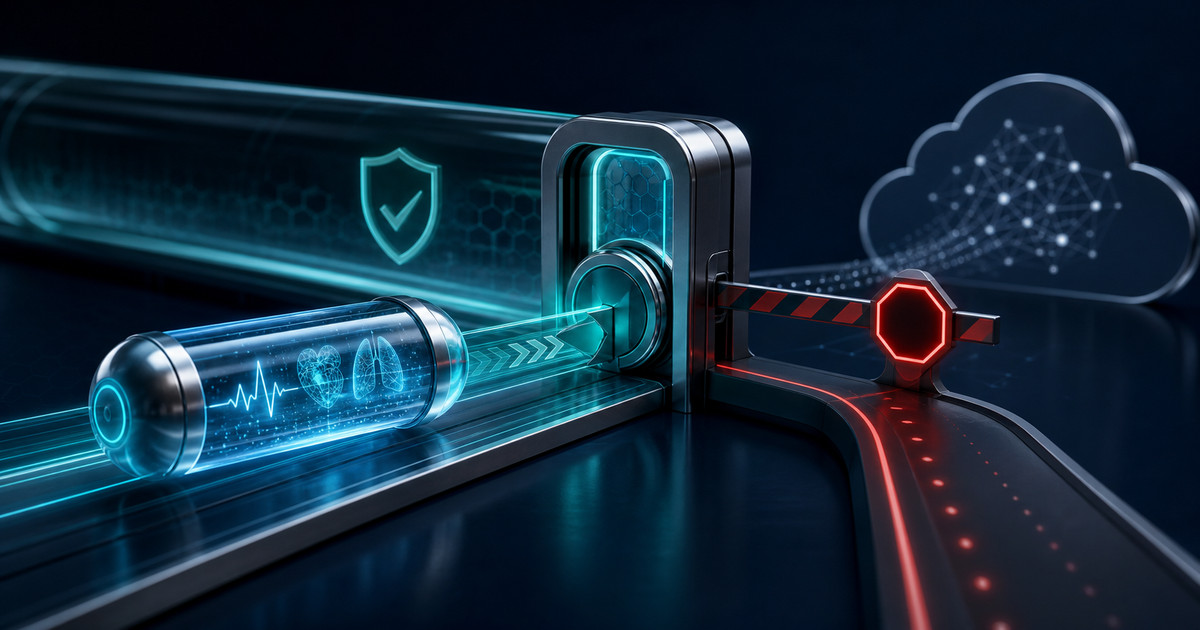
To keep medical data out of the wrong AI system, place a classification and routing gate before any model request leaves the organization. Maintain an approved-system register, block prohibited destinations, quarantine uncertain inputs and monitor attempts. Training alone cannot catch every pasted note, attachment or automated connector.
Block unsafe entry points
Inventory all ways a person or system can submit content: public chat tools, browser extensions, embedded assistants, application programming interfaces, email automations, support consoles and file uploads. Include unsanctioned tools that staff already use. A policy covering only the official application leaves the easiest escape routes untouched.
Classify information at the source when possible. The originating clinical or administrative system often knows more than a downstream text scanner. Preserve that label through exports and connectors. Where certainty is low, treat the item as restricted until a qualified owner decides otherwise instead of guessing from a few keywords.
Warnings should name the prohibited data and offer a safe alternative. If staff need an approved workflow but only receive a ban, they will search for a shortcut. Pair the message with access to the right system, a clear exception process and practical examples based on the organization’s own records and roles.
Route data by approved purpose
The approved-system register should name the owner, permitted purpose, allowed data categories, provider configuration, retention, training use, hosting path, user groups and review date. Approval belongs to that combination. A model accepted for drafting public text is not automatically accepted for analyzing a patient record.
A medical-data security implementation note can support architecture questions about isolation and controlled access. It cannot certify another environment, and its reported outcome should not become a promise. Verify the destination, configuration and workflow that will receive actual information.
Routing rules require tests at every interface. The precision release record is useful as an example of bounded test evidence. Apply that idea to blocked prompts, renamed attachments, copied tables, alternate accounts and connector retries, while remembering that a test suite is not legal approval.
Test escapes and incident response
Simulate realistic mistakes rather than obvious samples. Try partial identifiers, screenshots, compressed files, mixed public and restricted text, and an automated retry after a block. Confirm that quarantine preserves enough context for review without forwarding the protected content. Measure whether users can reach the approved route without abandoning the task.
Stage deployment by user group and connector. The staged go-to-market playbook offers a general gate structure that can limit exposure while controls prove reliable. It is not medical compliance guidance; the relevant principle is that evidence earns the next boundary.
Track the control as an operating metric without turning it into a vanity number. Review attempted restricted submissions, confirmed false positives, time to route an approved exception and destinations that generated repeated blocks. The purpose is to improve the safe path and close bypasses, not to punish users for revealing where the workflow is difficult.
Administrative approval needs its own boundary. A person able to add destinations should not quietly approve a personal integration without review. Log register changes, expire temporary exceptions and alert on a provider configuration that drifts from the approved record. This protects the routing decision after the initial project ends.
Review exceptions regularly and remove destinations that no longer serve an approved purpose. A stale approval is an open route, even when nobody remembers using it.
Frequently Asked Questions
Not necessarily. The answer depends on content, context, participants and applicable rules, so routing should handle uncertainty safely.
A warning helps, but prevention also needs approved tools, access controls, technical routing, monitoring and enforceable consequences.
No. Re-identification risk, residual details, provider terms and the intended purpose still require review.
Quarantine it, avoid sending it to the model, notify the user and route the case to an authorized reviewer.
If data reaches an unapproved system, revoke the route, preserve necessary logs, identify affected records, follow the organization’s incident process and obtain legal guidance on notification duties. Then fix the control that failed instead of relying on another reminder. An AI governance and agent audit can review intake gates, provider boundaries and response evidence.