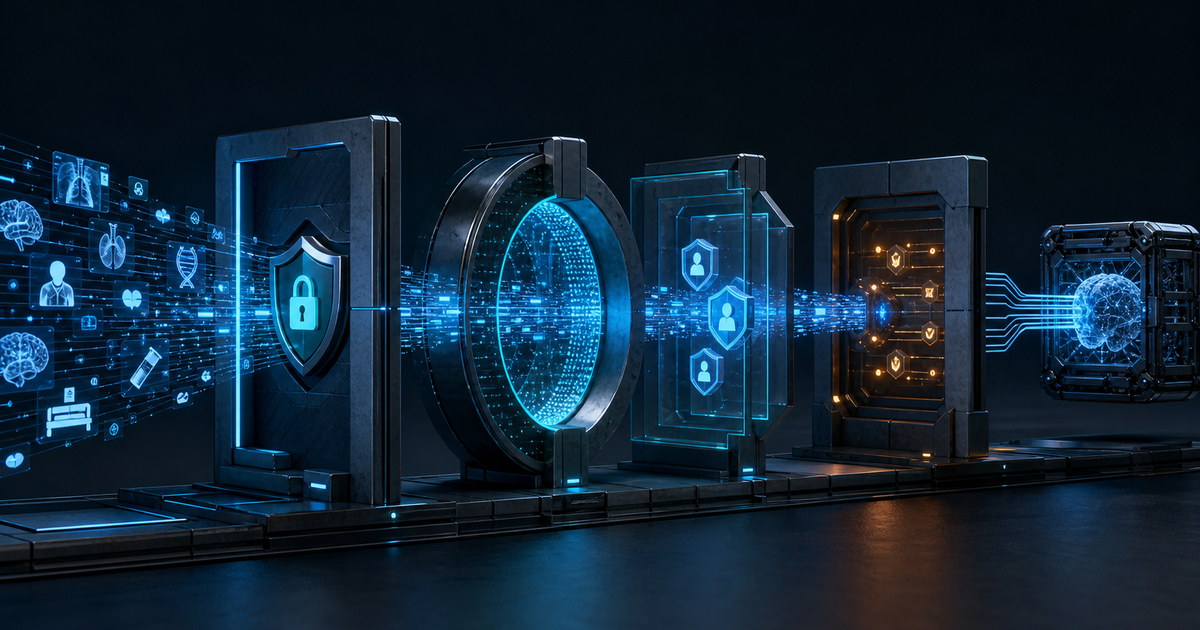
A medical AI integration can pass a product demonstration while its real data route remains unknown. Sensitive meaning may move through exports, prompts, logs, support tools, queues, replicas, and backups that were never included in the architecture review. Teams then face a difficult choice: delay the project after money has been spent or accept an exposure they cannot explain, revoke, or test.
AI4SALE provides a bounded security-readiness and remediation engagement before production medical data is connected. We trace the proposed route, inspect technical identities and vendor settings, translate approved policy into verifiable controls, exercise stop and recovery behavior, and return an evidence-backed connection verdict. The organization retains qualified legal, privacy, clinical, and security decision-makers. Our technical evidence does not create a blanket compliance certification or guarantee that an incident cannot occur.
The review tests the purchased and configured system
Generic architecture diagrams and vendor pages are useful starting points, but they do not establish the behavior of a specific account, tier, connector, region, or support arrangement. We follow each permitted field and derived artifact from its source to every processing and storage location. Human access, machine access, observability, deletion, and termination receive separate evidence.
The engagement distinguishes four outcomes. A control may be verified, verified with a stated limitation, blocked by missing evidence, or failed in the configured environment. Blocking or failed controls produce a remediation owner and retest requirement. They are not averaged into a broad readiness score.
AI4SALE connects the following work:
- Data-route discovery. We map source records, transformations, prompts, outputs, logs, support paths, and retained copies.
- Identity and permission testing. We verify allowed operations, denial behavior, secret ownership, revocation, and privileged access.
- Vendor configuration evidence. We compare purchased terms and enabled settings with the exact proposed boundary.
- Failure containment. We test stopping new work, isolating the connector, preserving approved evidence, and restoring the prior process.
- Residual-risk decision. Qualified owners receive the verified findings, limitations, open assumptions, and change triggers.
Early testing uses synthetic or prepared records when the task permits. Production data remains outside the integration until the required controls and destination evidence pass. If a requirement depends on unavailable vendor evidence or an unsupported configuration, the correct result may be a hold or architecture change.
Read Medical Data Security Before an AI Integration for the scheduled educational security framework. This companion is the commercial route for commissioning technical assessment, remediation, adversarial control tests, and an independent connection recommendation.
Buying questions about medical AI integration security
We return the verified data and identity map, control findings with evidence, remediation and retest records, unresolved assumptions, and a bounded connect, restrict, redesign, hold, or stop recommendation.
We compare the approved requirement with account settings, identities, permitted and denied operations, logs, retention and deletion behavior, failure tests, and destination evidence for the named configuration.
Typical inputs include the proposed data route, system and service identities, vendor tier and terms, enabled settings, retention and support configuration, approved policies, incident owners, and safe test-environment access.
We record the missing evidence and affected decision, then propose restriction, compensating control, architecture change, vendor escalation, or a hold. Production data is not connected simply to preserve a schedule.
Yes, when it can inspect every service boundary, obtain the required vendor evidence, run controlled failure and recovery tests, involve qualified privacy and clinical owners, and separate implementation from final acceptance.
Open the medical integration security pack with a work email
Medical AI Integration Security Assessment Pack
Enter your work email and the Implementation guide for Verify Medical Data Security Before Connecting AI will open immediately below on this page. You do not need to visit your inbox.