Email is rarely one clean input. A business mailbox mixes customer requests, internal approvals, signatures, attachments, automated notices, sensitive threads, and malicious content. Giving an AI workflow broad mailbox access can turn a narrow automation goal into an uncontrolled identity and data problem.
AI4SALE implements email-to-AI routes with a defined message population, minimum access, normalized records, untrusted-content handling, review boundaries, and delivery evidence. We start from one business outcome, such as preparing a reply for approval or classifying an eligible request. We do not begin by handing a model an entire mailbox.
The integration is designed as a controlled message route
The engagement begins with the account, folders or labels, sender population, message types, attachments, and downstream destination that belong to the use case. Personal mail, privileged discussions, unrelated departments, and unsupported file types remain outside the route. Where the provider permits it, the connection uses a dedicated service identity or the narrowest delegated scope available.
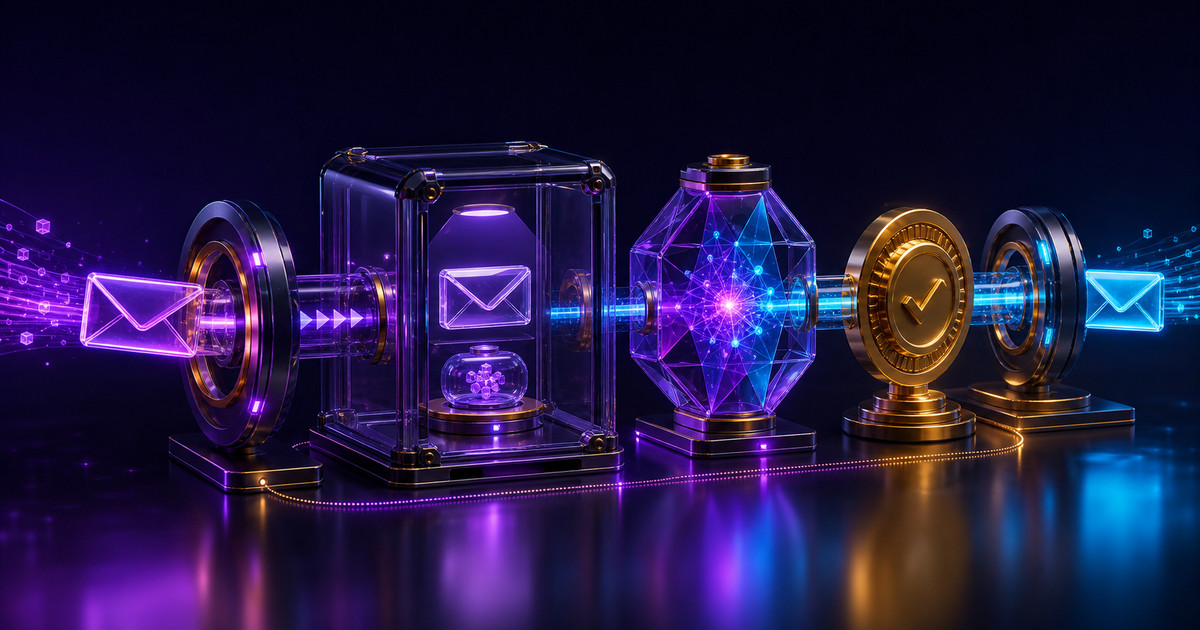
AI4SALE then builds six operating layers:
- Selection boundary. Only messages matching approved account, location, sender, recipient, and purpose rules enter processing.
- Canonical message record. The route preserves stable message identity, thread context, timestamps, recipients, attachment references, and the original source.
- Content trust boundary. Email text and attachments are treated as untrusted business data, not instructions that may expand tool or data access.
- Decision separation. Classification, extraction, summarization, and drafting have distinct output schemas and permission limits.
- Human release control. Replies, CRM changes, forwarding, and other external effects stay behind the required approval and policy checks.
- Operations evidence. Every accepted, rejected, duplicated, delayed, and failed message receives a traceable disposition.
The design depends on the buyer’s email platform, identity setup, retention policy, security requirements, and business process. AI4SALE will not claim universal compatibility before inspecting those boundaries. If a safe route cannot be created with the available account controls, we return that constraint instead of masking it with an application password or an overprivileged credential.
Read Connecting Email to AI: Secure Architecture and Access Boundaries for the scheduled architecture overview. This page is the procurement path for a company that wants AI4SALE to design, connect, test, and hand over a working email automation.
Procurement questions for an email-to-AI integration
Prioritize it when a defined class of messages creates recurring triage, extraction, drafting, or routing work and the business can name the owner, accepted result, and downstream destination.
We exercise approved and excluded messages, duplicate delivery, broken attachments, malicious instructions, access denial, delayed dependencies, reviewer rejection, and destination read-back. Each case receives an observed result and evidence reference.
We need the business purpose, mailbox and identity owner, sample eligible and excluded messages, attachment inventory, retention rules, downstream field expectations, approval owner, and the platform controls available for minimum access.
Blockers include mailbox-wide access with no narrower route, mixed personal and business identity, unclear retention authority, no owner for false routing, an unsupported attachment path, and an external action that cannot be reviewed or reversed.
An internal build is realistic when the team can manage email identity, minimum scopes, message normalization, content security, downstream contracts, replay protection, review operations, monitoring, and incident recovery as one owned service.
Enter a work email to open the Email-to-AI Control Pack
The protected pack includes the mailbox scope register, message contract, content-risk matrix, action permissions, exception runbook, cutover checks, and acceptance record for one controlled integration.
Email-to-AI Integration Control Pack
Enter your work email and the Implementation guide for We Connect Business Email to AI Without Mailbox-Wide Control will open immediately below on this page. You do not need to visit your inbox.