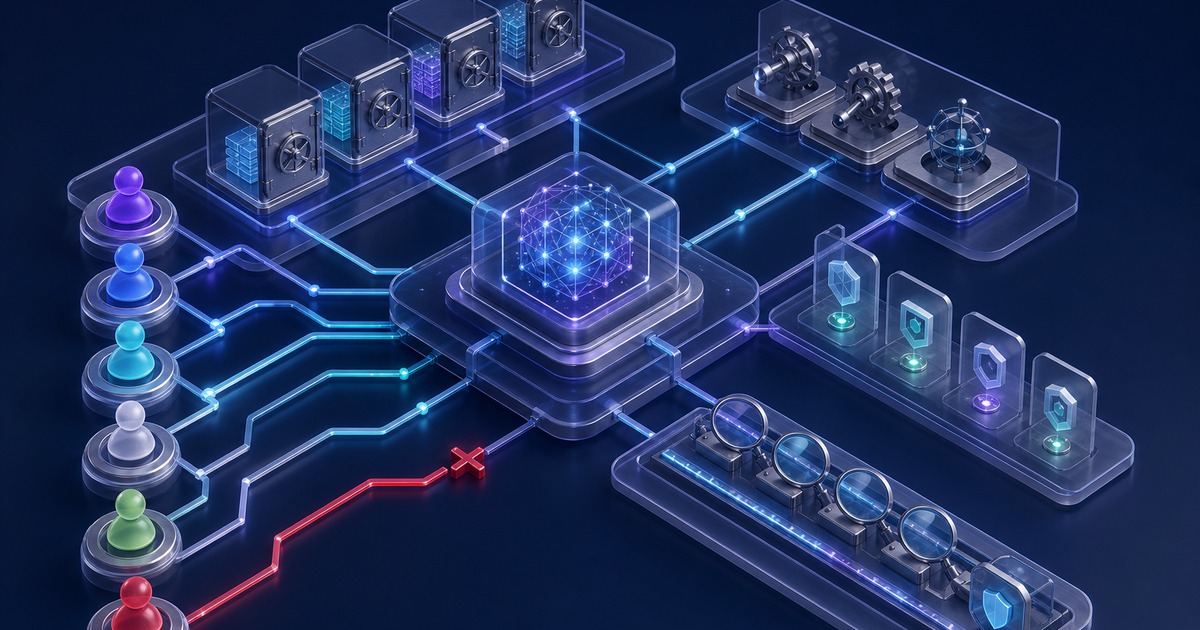
A role and permission matrix for enterprise AI should answer six operational questions: who can see the data, who can ask the model, who can call a tool, who can approve the result, who can audit the evidence, and who can stop the system. Job titles alone cannot answer them.
Build the matrix for one workflow at a time. A support assistant, contract reviewer and payment agent may share infrastructure while requiring completely different data fields, tools and human authority.
Define permissions around actions, not applications
Use rows for business owner, system owner, data steward, operator, reviewer, risk or legal specialist, security responder and independent auditor. Add vendor support and service identities where they can touch the process. Every row needs a named accountable person even when several people perform the work.
Use columns for view source, retrieve context, submit prompt, change instruction, select model, connect data, call tool, create draft, execute action, approve, override, inspect logs, export evidence and disable service. This exposes dangerous combinations hidden inside a broad administrator role.
Company knowledge deserves a separate boundary. The company memory architecture beyond vector search shows why source authority, retrieval representation, permissions and observed outcomes should not collapse into one shared store.
Add scope beside every permission: entity, customer, department, jurisdiction, data class, environment and effective period. A person may approve a sales draft for one entity without gaining access to another entity’s contracts or private notes.
Attach a lifecycle to each grant. The request states the business task and duration, the approver checks conflicts, the platform applies the narrow scope, and a later review confirms continued need. Ownership changes, leave, contract expiry and workflow retirement should revoke access without waiting for an annual audit.
Separate proposal, approval and execution
An agent may propose a change without permission to perform it. A human reviewer may approve within a value or risk limit. A separate execution identity carries out the accepted action and writes a receipt. This separation makes intent, authorization and effect independently visible.
High-consequence tools need an allowlist of operations and parameters. A calendar agent may create a draft invitation but not delete a schedule. A finance assistant may prepare a reconciliation but not release a payment. A retrieval agent may cite an approved source but not broaden its own access.
Define negative permissions explicitly. The trust checklist for confident AI failures helps test whether the system withholds, asks for evidence or escalates when it reaches a knowledge or authority boundary.
Break-glass access requires a reason, short expiry, strong authentication, notification and retrospective review. The emergency user must not be the sole reviewer of its own actions. Revocation should propagate to cached sessions, tokens, indexes and downstream tools.
Test the matrix as an adversary and an operator
Create cases for valid access, wrong department, cross-customer similarity, moved employee, expired contractor, revoked approver, compromised service account and unavailable owner. Confirm both denial and the legitimate escalation path. Security that only blocks work will be bypassed.
Test changes as well as steady state. When a role, model, data source or tool changes, identify the affected matrix cells and rerun their acceptance cases. Log policy version, identity, decision, evidence, action and final system state.
Outcome metrics also need permission boundaries. The three checks for invented AI metrics support a simple rule: an agent may summarize approved measurements but cannot create an observation that never occurred.
AI4SALE’s integration checklist includes role-based access, audit, source reliability and escalation. It supports the matrix method described here without proving that any customer’s access design has passed an external audit.
Frequently Asked Questions
It covers the workflow roles, data scopes, model use, tool actions, approval, audit, revocation and emergency shutdown.
A title rarely states which customer, dataset, model, parameter, action or approval threshold is allowed in a specific process.
High-consequence work should separate proposal, approval and execution so authorization and effect remain independently reviewable.
Retest after role, source, model, tool or policy changes and during scheduled reviews of privileged and temporary access.
For a workflow-level permission review and adversarial acceptance set, use the AI governance and agent audit service. The deliverable should name every high-risk permission, owner and revocation test.