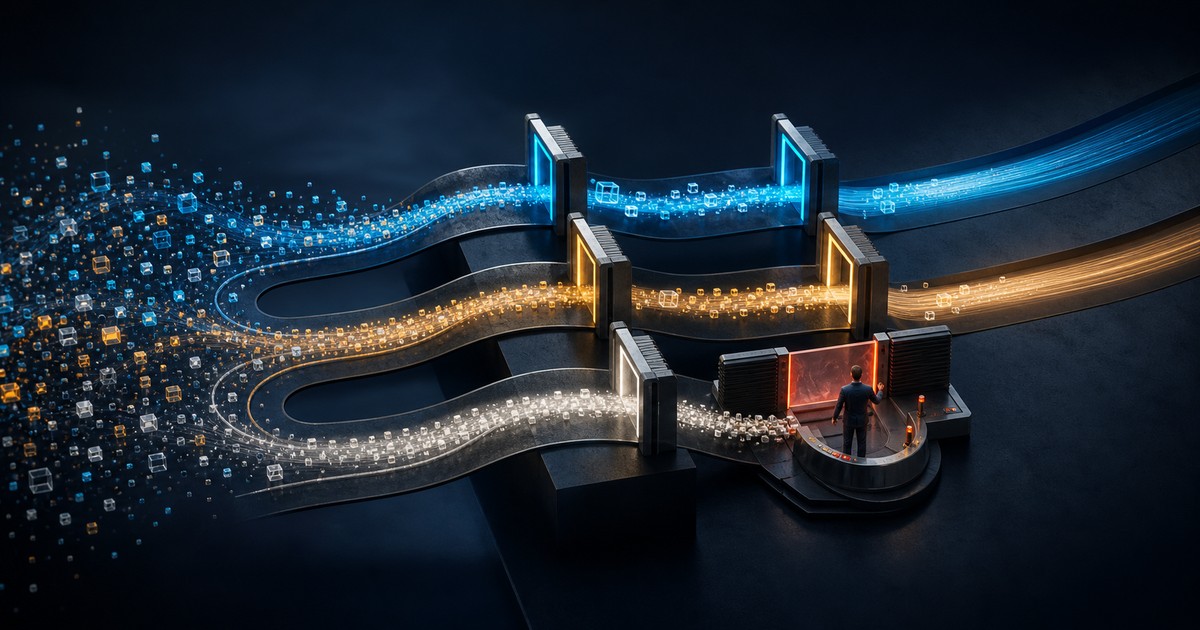
AI governance for a company that needs to move fast should reduce repeated debate, not add a committee to every task. The practical model is a set of decision lanes. Low-impact, reversible work moves under predefined rules. Actions that affect customers, money, access, personal data, or production systems require stronger evidence and a named approver. Teams gain speed because the boundary is clear before a deadline arrives.
Govern the decision, not the technology label
Start with the business outcome and the action an AI system can take. Drafting an internal note is different from sending a customer message. Reading a record is different from changing it. For each workflow, name the owner, data source, allowed operations, prohibited operations, and the condition that stops execution. This produces a usable control surface instead of a broad policy about responsible AI.
Knowledge also needs an accountable source. The guide to company memory beyond vector search explains why retrieval alone is not enough when teams need provenance, boundaries, and conflict handling. A fast workflow should carry the source reference and policy version into the decision record, so a reviewer can understand what the agent relied on.
Divide actions into operating lanes by consequence and reversibility. An allowed lane can run automatically within narrow permissions. A monitored lane can run while selected cases receive review. A controlled lane pauses for approval because the action creates an external commitment or a difficult recovery. A prohibited lane remains unavailable regardless of model confidence.
Make every control executable
A rule such as use human oversight is too vague. State who reviews, what evidence appears, how long the decision remains valid, and what happens when nobody responds. The approval packet should show the requested action, affected object, source evidence, policy result, expected consequence, rollback option, and any unresolved uncertainty.
Confidence must not substitute for verification. The founder trust checklist for confident AI failures is relevant because it focuses attention on checking outputs that sound finished. Build that challenge into the workflow through independent data checks, tool receipts, and a reviewer who can reject the preferred answer.
Permissions should match the lane. Use separate service identities, narrow scopes, explicit tool allowlists, and time-limited elevated access. Log reads, proposed actions, approvals, executions, and failures with a shared correlation identifier. The operating rule is direct: no access without limits, and no limits without logs.
Review exceptions before they become policy
Keep a small portfolio register of active AI workflows. It should show the business owner, current lane, connected systems, sensitive data, unresolved risks, recent exceptions, and next review trigger. Review material changes rather than scheduling ceremonial approval for unchanged low-risk work.
Metrics need the same discipline. The article on agents inventing metrics shows why a neat number still needs source, scope, and recomputation. Governance measures should therefore come from system events: blocked actions, overridden decisions, missing receipts, stale policies, and recovery failures. Avoid vanity counts of models or prompts.
When an exception is approved, record its owner, reason, duration, affected workflow, compensating control, and expiry. Do not let an urgent workaround silently become permanent access. This is how governance preserves speed: routine work follows known lanes, while genuine changes receive focused attention from the people authorized to accept the consequence.
Make lane definitions part of delivery acceptance. Before a workflow enters regular use, ask the receiving team to classify several ordinary and difficult cases, explain the chosen route, and demonstrate the stop condition. Then test a policy change and a failed dependency. If operators cannot predict whether an action will run, wait, or stop, the lane is not ready. Publish the current decision table where product, security, and operations can inspect the same version. Changes should identify the owner, reason, effective date, affected workflows, and rollback path. This small discipline prevents two teams from applying different boundaries to the same business action.
Frequently Asked Questions
It pre-defines which actions may proceed, which need monitoring, which require approval, and which remain prohibited, reducing repeated case-by-case debate.
Prioritize actions that affect customers, payments, access, personal data, legal commitments, production systems, or anything difficult to reverse.
Show the proposed action, affected object, source evidence, policy result, expected consequence, rollback option, and unresolved uncertainty.
Record the owner, reason, scope, compensating control, duration, and expiry, then revoke the temporary access when the exception ends.
To map decision lanes, permissions, evidence, and ownership across a live portfolio, use an AI governance and agent audit before exceptions accumulate.