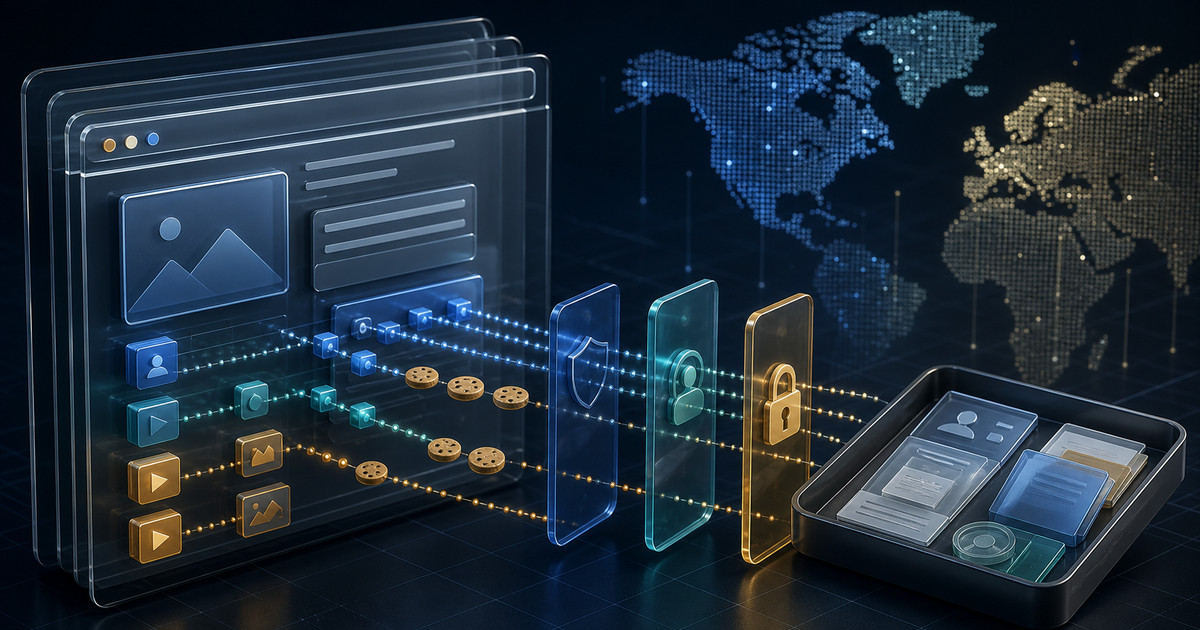
Website privacy compliance across the United States, Canada and Europe should be audited by observing what pages actually collect and transmit, then comparing that behavior with notices, visitor choices and internal procedures. A polished policy cannot correct a form, pixel or embedded tool that sends unexpected personal information.
Inventory actual browser behavior
Crawl representative page types and test them manually. Include landing pages, account creation, checkout, contact forms, newsletters, careers, support, embedded video and authenticated areas. Record cookies, local storage, network requests, form destinations and server-side events. Repeat the observation before and after each available privacy choice.
Open the tag manager and vendor list, but do not assume configuration names describe reality. A dormant tag may still fire on an overlooked template, while a server-side integration may never appear in the banner inventory. Reconcile browser evidence, source configuration, vendor contracts and the team’s stated purpose for each collection.
For the United States, applicability can depend on state, business and activity; California’s consumer privacy regime is one important example, not a national substitute. Canada requires its own private-sector analysis. European Union GDPR duties and United Kingdom rules, including electronic communications requirements, also need separate treatment.
Test notices and controls by visitor context
Compare the first-layer message, detailed notice and preference panel with observed behavior. Check whether rejection is as usable as acceptance, whether a saved choice persists and whether newly added tags respect it. Also test visitors arriving through campaigns, translated pages and logged-in sessions, because those routes often load different integrations.
A medical-data security implementation note can remind auditors that the sensitivity of a form changes the required scrutiny. It does not certify a website. A symptom field, appointment request or insurance detail requires a different risk discussion from an ordinary newsletter address.
Website assets can reveal overlooked obligations. The font license risk audit demonstrates a concrete discovery method for third-party files and their sources. Apply comparable evidence gathering to scripts, embeds and pixels instead of relying on the marketing team’s remembered vendor list.
Turn findings into release tickets
Each finding should state the page, visitor context, observed request, data fields, recipient, expected behavior and evidence needed for closure. Assign both a technical owner and a policy owner where the fix changes wording or purpose. Severity should reflect sensitivity, scale of exposure, user choice and ability to stop the transfer.
Regional comparisons outside the target markets can reveal reusable engineering weaknesses without supplying legal authority. The UAE website privacy risk discussion reinforces the operational need to connect notices with actual trackers. Use local official sources and counsel for the United States, Canada and Europe.
Rights workflows deserve the same end-to-end test as tracking choices. Submit a representative access or deletion request, verify identity handling, follow the request through form tools and customer systems, and confirm the final response. A web link that opens a mailbox is not a working rights process if no owner can locate the related records.
Test the mobile experience and accessibility of privacy controls. A choice that sits off-screen, uses unreadable contrast or requires confusing extra steps may fail users even when the code records it correctly. After a visitor changes a preference, confirm that later page loads and server-side events follow the new state.
Preserve a compact audit trail with screenshots, request records and configuration references. Evidence should be sufficient for retesting without storing more visitor information than the review requires.
Frequently Asked Questions
No. The published notice must match actual collection, tracking, sharing, retention and user-rights operations.
Not automatically. Visitor location, applicable rules and the technologies used may require different controls and wording.
Check tag managers, embedded media, chat tools, advertising pixels, error logs, form integrations and server-side events.
Create reproducible tickets with page, visitor context, observed request, expected behavior, owner and acceptance test.
Retest the exact path after remediation and preserve a short evidence record. Then add recurring checks for tag changes, new forms and vendor updates so compliance does not decay after launch. For a page-level review that joins technical behavior with governance controls, request an AI governance and agent audit.