Small and midsize businesses rarely need a year-long governance program before they can reduce immediate AI exposure. They need one important workflow brought under control without freezing useful work. The challenge is delivery capacity: the same people who know the process are serving customers, running operations, and maintaining the systems that an assessment would ask them to change.
AI4SALE provides a 30-day implementation focused on one high-consequence AI workflow. We discover its real operating path, make priority control changes, test failure and recovery, and leave owners with evidence and a sequenced follow-on backlog. The engagement is a bounded security improvement, not a compliance certificate or a claim that incidents cannot happen.
A month works when the outcome is narrow and operational
The first decision is not which policy template to adopt. It is which workflow deserves the month. Good candidates touch customer or employee data, use reusable credentials, publish or send externally, affect access or money, depend on a single supplier, or have no reliable manual fallback. We score candidate workflows and agree on one release boundary before implementation begins.
The delivery sequence is designed around visible weekly outcomes:
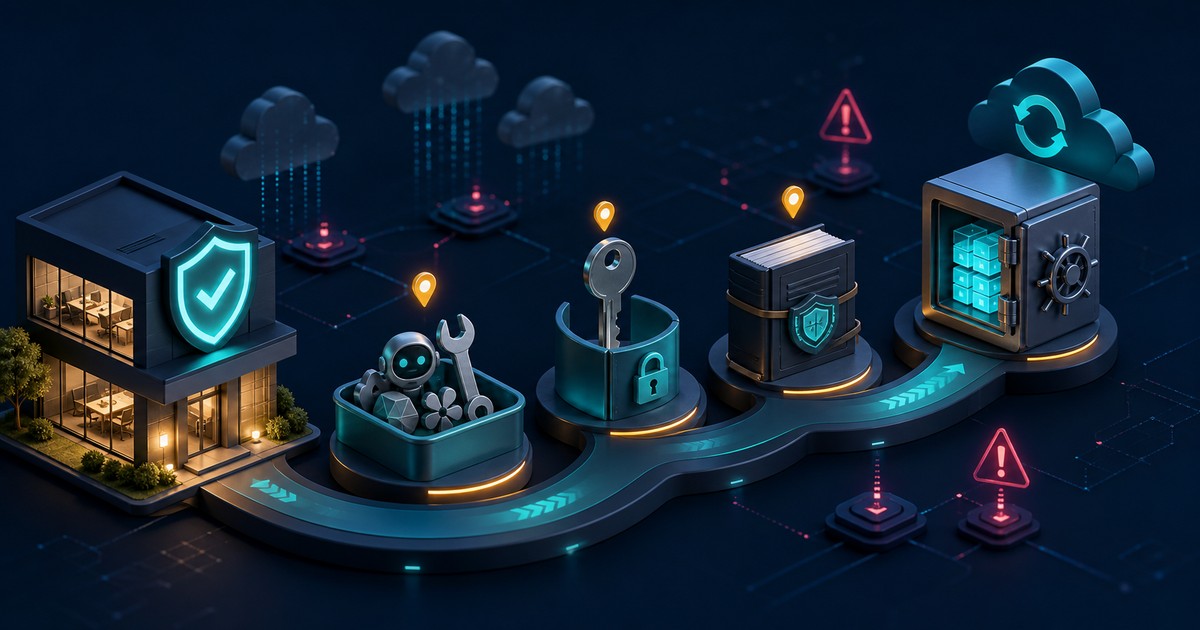
- Exposure baseline. We identify the people, systems, identities, data, vendors, external actions, and owners inside the chosen workflow.
- Containment changes. We remove unnecessary access, separate identities, narrow data movement, add decision controls, and pause paths that lack authority.
- Evidence and detection. We create useful action receipts, monitoring signals, escalation ownership, and a risk register without turning logs into a sensitive-data archive.
- Failure rehearsal. We exercise denial, incorrect output, unavailable dependencies, stopped integrations, and the approved fallback process.
- Operating handoff. We deliver acceptance results, residual limits, owners, maintenance triggers, and the next set of prioritized improvements.
The buyer remains the authority for access, business decisions, and risk acceptance. AI4SALE implements only the approved boundary and records any condition that prevents a safe change. If the selected workflow cannot be mapped, lacks an owner, or depends on an unavailable supplier change, we surface the blocker instead of substituting policy prose for working controls.
Read A 30-Day Security Plan for an AI-Enabled SMB for the scheduled educational sequence. This companion is for leaders who want a provider to execute and verify the highest-value portion of that work.
Buying questions for a 30-day AI security engagement
A realistic scope covers one important workflow: its exposure map, priority permission and data controls, useful evidence, recovery exercise, residual-risk decisions, and an owned follow-on plan. It does not secure every AI use across the company.
We inspect configured state, run allowed and denied cases, interrupt dependencies, exercise the fallback, read back target-system results, and issue a verdict for the tested workflow revision.
We need a business owner, technical owner, security contact, representative non-sensitive test cases, redacted configuration and traces, access to the approved test environment, and named authority for each proposed change.
The common blockers are an undefined workflow, unavailable owners, unknown credentials, no testable environment, vendor dependencies, changes without rollback, and an attempt to cover the entire company instead of one bounded operating path.
Provider support is optional when the business has protected delivery time, authority across the workflow, security and engineering capability, an independent acceptance reviewer, and the ability to change and test live integrations safely. AI4SALE fills missing delivery and coordination capacity.
Enter a work email to open the 30-day delivery pack
The protected pack contains the selection scorecard, weekly workboard, exposure register, control change record, recovery exercise, acceptance matrix, and executive handoff used for one bounded implementation.
30-Day AI Workflow Security Delivery Pack
Enter your work email and the Implementation guide for We Secure Your Highest-Risk AI Workflow in 30 Days will open immediately below on this page. You do not need to visit your inbox.