-
We Replace Agent-Visible Secrets With Controlled Service Access
AI4SALE replaces one agent credential path with constrained service operations, approval binding, controlled cutover, adversarial tests, and recovery evidence.
-

Commission an Investor Reporting Dashboard Your Team Can Defend
AI4SALE turns one investor reporting event into a controlled dashboard with source lineage, approval states, audience permissions, correction handling, and release evidence.
-
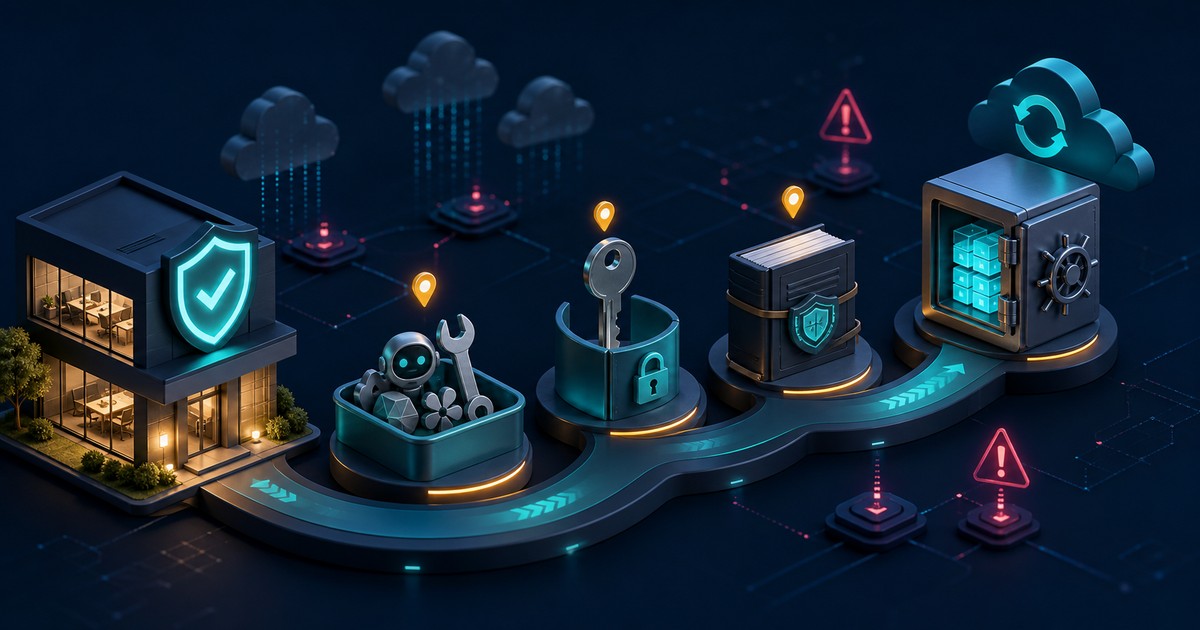
A 30-Day Security Plan for an AI-Enabled SMB
A practical month-long plan reduces the highest-consequence AI risks before adding heavier controls.
-
The Legal and Security Risks Hidden in AI Vendors
AI vendor review must connect contract language to actual data flows, controls, incident duties, and exit options.
-
We Choose and Prove the First AI Workflow Before You Scale
AI4SALE turns current operating evidence into one qualified AI opportunity, a permission-bounded pilot, representative tests, and a clear build or stop decision.
-
Business Continuity for AI-Dependent Operations
AI continuity depends on known dependencies, degraded modes, manual fallbacks, and tested recovery decisions.
-
What to Log When AI Touches Sensitive Data
Useful AI logs explain who accessed sensitive data, why, what happened, and whether the action was accepted.
-
Deploy Codex in Your Engineering Team With Release Controls
AI4SALE establishes one governed Codex delivery lane with durable context, bounded authority, runnable checks, independent review, and a controlled rollout.
-
Threat Modeling an AI Agent With Tool Access
A tool-using agent needs a threat model built around capabilities, trust boundaries, and recoverable actions.
Start your project
Tell us what you want to build
Describe the website, automation, or digital service you need and the result it should deliver. Add your contact details. We will reply with a practical next step.
Send your project details