Enterprise AI access often grows through application roles that are too broad for the decisions being automated. A user who can open a workspace may also reach data, change instructions, connect a tool, approve an output, or export evidence. When those powers are hidden inside an administrator label, ownership reviews and incident response cannot establish what was actually authorized.
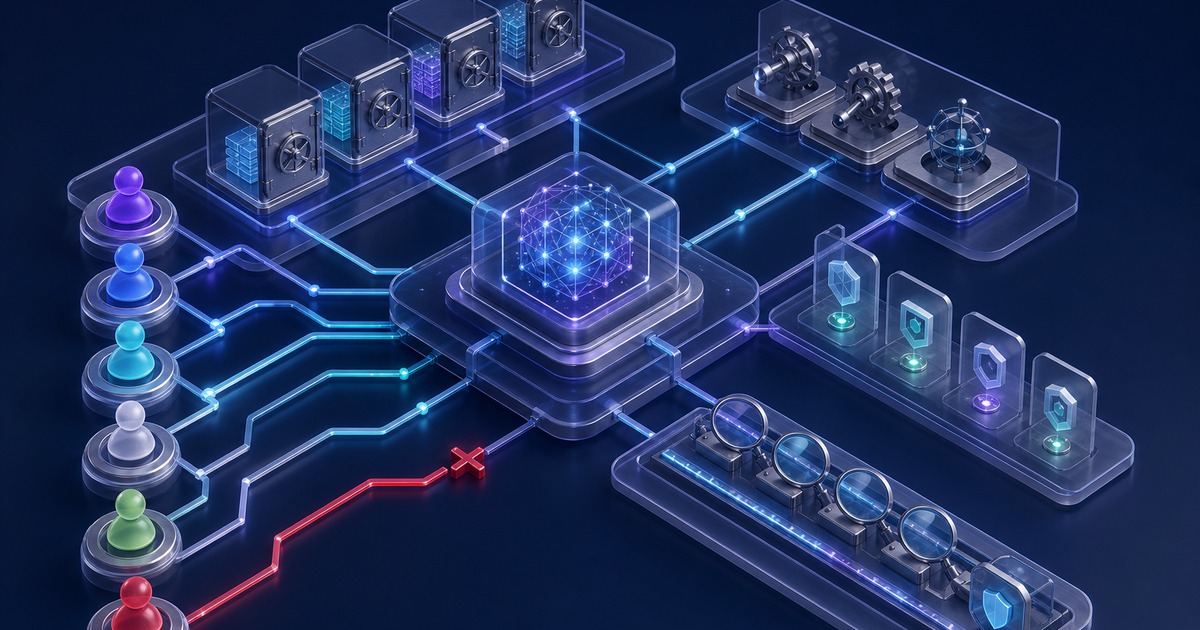
AI4SALE implements a workflow-level permission system. We map people and service identities to data, model, tool, approval, audit, and shutdown powers; configure the narrowest practical controls; establish grant and revocation routes; and test both denial and legitimate escalation. Business, security, legal, and data owners retain authority for the access decisions.
The design follows an action from request to effect
A practical matrix distinguishes seeing a source, retrieving context, drafting, proposing a tool call, approving it, executing it, reviewing evidence, and disabling the service. Scope includes entity, customer, department, environment, data class, amount or consequence threshold, and effective period. This makes dangerous combinations visible before configuration begins.
The scheduled guide A Role and Permission Matrix for Enterprise AI describes the informational model. AI4SALE’s engagement turns it into identity mappings, enforcement rules, approval routes, lifecycle automation, evidence, and adversarial acceptance tests.
Access must remain operable when people and systems change
The implementation covers joiners, movers, leavers, temporary access, service accounts, delegated approval, unavailable owners, emergency access, supplier support, and cached credentials. Every grant has a purpose, approver, scope, expiry or review trigger, and evidence of application. Revocation is tested at downstream tools, not merely marked complete in a ticket.
The first release targets one workflow with consequential data or actions. It confirms that valid work still reaches its destination, unauthorized combinations fail closed, and an operator has a usable escalation path. AI4SALE does not declare the resulting design compliant with every requirement or replace the buyer’s access authorities.
Buying questions about enterprise AI permissions
Before connecting sensitive data or consequential tools, and whenever a pilot becomes an owned service, crosses entities, adds service identities, or changes approval authority.
We test allowed work, wrong scope, revoked roles, expired contractors, unavailable approvers, service-account misuse, emergency access, and downstream revocation while checking both decision and final system state.
Typical inputs include the workflow, identity providers, current roles, data classifications, tool operations, approval thresholds, system owners, employment events, vendor access, logs, and a safe acceptance environment.
Shared accounts, application-wide roles, hidden service identities, self-approval, missing expiry, incomplete downstream revocation, uncontrolled emergency access, and no escalation path for legitimate work create avoidable gaps.
Yes, if identity, application, data, security, business, and audit owners can change configuration and independently test it. AI4SALE helps when permissions span platforms or ownership is fragmented.
Enter a work email to open the permission design pack
The protected package contains an action inventory, role matrix, grant contract, separation rules, emergency model, revocation map, adversarial tests, and operational handoff.
Enterprise AI Permission Design Pack
Enter your work email and the Implementation guide for Install Enterprise AI Permissions Around Real Actions will open immediately below on this page. You do not need to visit your inbox.